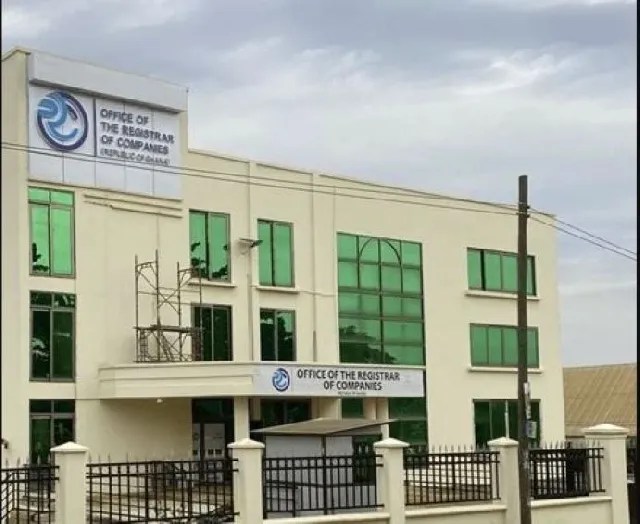
Imagine this: a government agency tasked with regulating compliance is itself handed a stern lesson in following the rules. That’s exactly what happened in Ghana when the Office of the Registrar of Companies (ORC) found itself fined GH¢240,000 for a cybersecurity oversight. It’s a case that doesn’t just highlight regulatory gaps—it exposes the uncomfortable truth that even institutions with authority can stumble when it comes to adhering to their own legal frameworks. What makes this particularly fascinating is how it underscores the growing tension between bureaucratic inertia and the urgent need for cybersecurity accountability in an age where digital vulnerabilities can cripple entire economies.
Let’s unpack this. The ORC, a critical player in Ghana’s business ecosystem, was slapped with a hefty penalty for hiring Purpleline Solutions, a cybersecurity firm that hadn’t secured the necessary license. The Cyber Security Authority (CSA) wasn’t just handing out a fine; it was delivering a wake-up call. Here’s the kicker: the ORC had been explicitly told to engage only Tier 1 licensed providers. Yet, despite this directive, they pressed ahead, treating the rules like a suggestion. Personally, I think this reflects a deeper issue—how even well-intentioned organizations can prioritize speed or cost over compliance, especially when the consequences of a breach aren’t immediately visible. It’s like driving without a seatbelt because you’ve never had an accident. The problem, of course, is that the next incident could be catastrophic.
Now, let’s talk about Purpleline. The company wasn’t just unlicensed; it applied for its license after being hired by the ORC. That’s not just procedural negligence—it’s a glaring example of regulatory roulette. The CSA made it clear that an application isn’t a green light. But here’s what many people don’t realize: in the fast-paced world of cybersecurity, companies often rush to secure contracts before formalities are complete. What this really suggests is a systemic disconnect between the urgency of securing systems and the deliberate, sometimes slow, process of licensing. It’s a race against time, and in this case, Purpleline lost badly. The fine of GH¢120,000 isn’t just a punishment; it’s a warning to other firms that shortcuts won’t be tolerated. The question is, will they heed it?
The CSA’s response to this incident is telling. They’re not just fining entities—they’re issuing a broader challenge to the entire ecosystem. Public-sector organizations, private firms, and even individuals are now under the microscope. The authority’s message is clear: cybersecurity licensing isn’t a formality; it’s a legal cornerstone. But here’s the rub: how do you enforce such rules in a landscape where expertise is scarce and demand is high? I’ve seen this dynamic play out in other countries, where the pressure to hire ‘qualified’ providers leads to a gray market of unlicensed but competent firms. Ghana’s approach is strict, but it raises a provocative question: is it better to have a few licensed experts or a flood of unregulated ones? The answer, I think, lies in the long-term stability of critical infrastructure. A single breach at the ORC could ripple through the entire business environment, eroding trust in digital systems.
What this case also highlights is the psychological burden on institutions. The ORC, as a regulator, is now in the position of being regulated. It’s a humbling reminder that no one is above the law—even if you’re the one writing it. This isn’t just about money; it’s about credibility. If the ORC can’t follow its own rules, how can it expect others to? It’s a leadership crisis in disguise. And yet, there’s a silver lining: this incident could become a catalyst for stricter internal compliance protocols. Imagine a future where every public agency has a dedicated cybersecurity compliance officer, someone whose job is to ensure that no shortcuts are taken. That’s not just possible—it’s necessary.
Looking ahead, this fine could set a precedent. Will other institutions double down on due diligence, or will they see this as a one-time glitch? I suspect the latter. Compliance fatigue is a real thing, especially when the stakes feel abstract. But here’s what I find interesting: the CSA’s emphasis on verifying both licensing status and tier level suggests a nuanced understanding of cybersecurity risk. Tier 1 providers aren’t just licensed—they’re vetted. This implies a hierarchy of security standards, which is both logical and necessary. However, it also creates a potential bottleneck. If only Tier 1 firms can handle critical infrastructure, what happens when demand outpaces supply? Will we see a surge in new providers scrambling to meet the licensing criteria, or will the market remain tightly controlled? The answer might shape Ghana’s cybersecurity landscape for years to come.
In the end, this isn’t just about a fine. It’s about the evolving relationship between regulation and innovation. The CSA’s actions signal a shift toward a more proactive, less forgiving approach to cybersecurity. But as someone who’s watched similar regulatory battles unfold, I can’t help but wonder: will this be the turning point that forces systemic change, or will it be remembered as a cautionary tale of missed opportunities? The truth is, we’re all navigating uncharted territory here. The only thing certain is that the cost of inaction is far higher than the price of compliance.